
“The audit I can't answer, and the register I rebuild from scratch every single year.”
Stop rebuilding your audit evidence — you already have it.
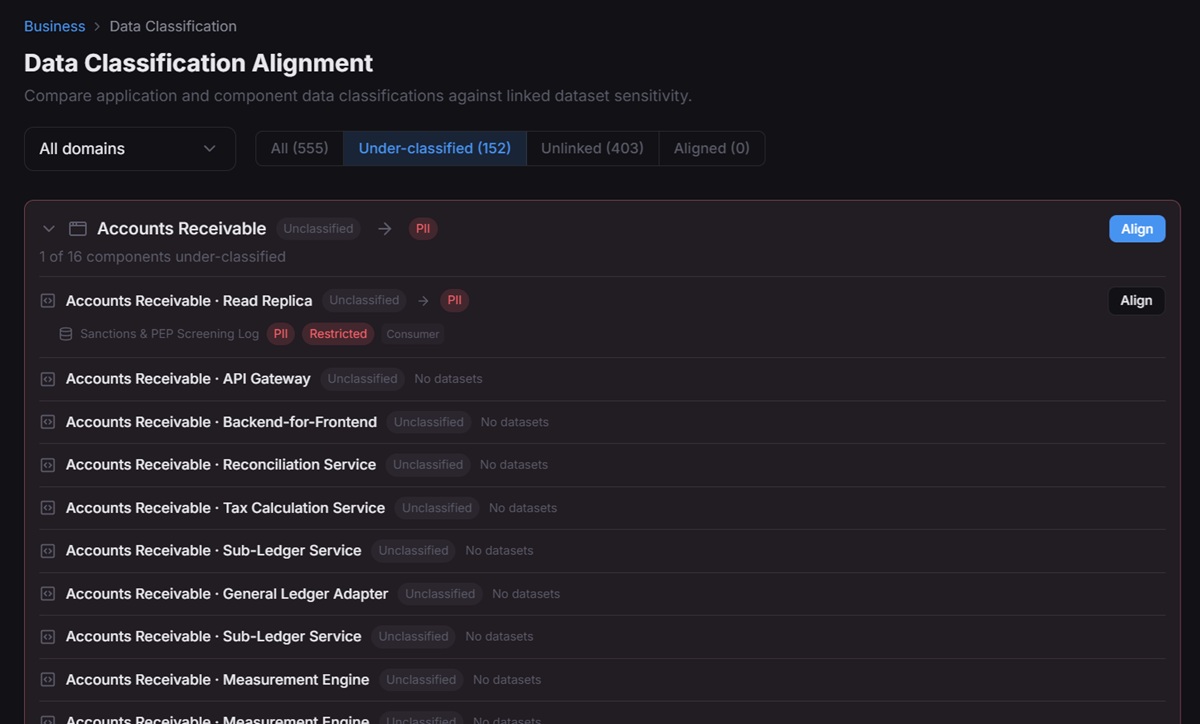
The same model that computes blast radius reads, unchanged, as the artifacts your auditors demand — grounded in named, verifiable fields and cited to specific articles, never a certification badge.
One model, read four ways
Your application and component inventory feeds an ISO 27001 Annex A.8 asset register. Your Datasets — with classification, legal basis, retention and regulatory exposure as first-class fields — form the structured backbone of a GDPR Article 30 Record of Processing, and their ICT-data documentation supports DORA's Article 28 third-party oversight.
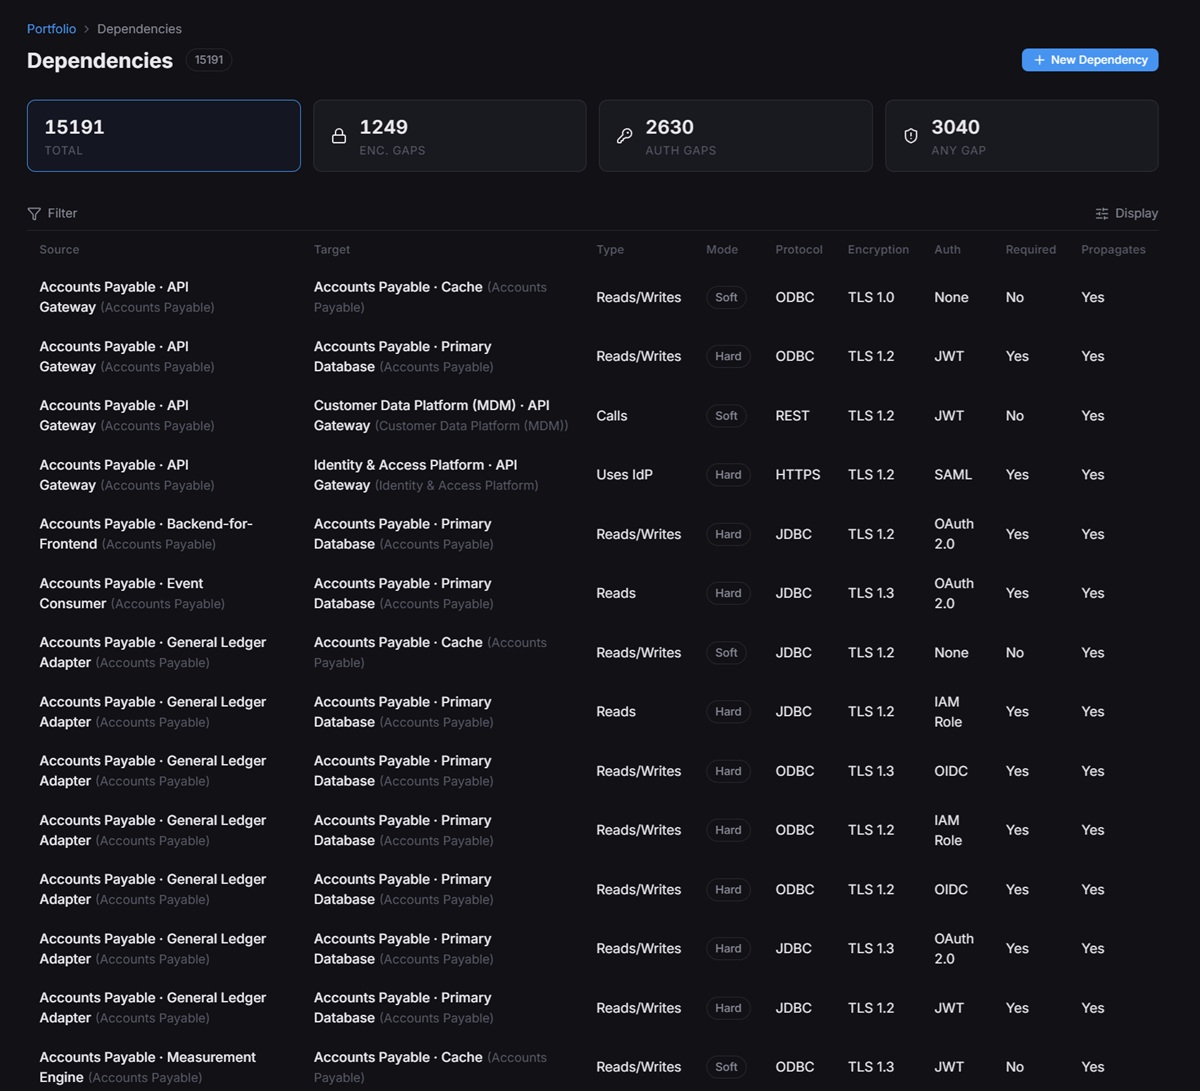
Every dependency edge records its transport encryption and endpoint auth, so unencrypted paths and unauthenticated interfaces surface as findings — the evidence ISO 27001, NIS2 Article 21 and GDPR Article 32 all make you produce. When a regulator asks, you filter and show instead of assembling a spreadsheet.
Backed by real fields, not a bolt-on module
Data lineage for your DPIA
Data Lineage maps exactly where pii, phi and financial data flows — the data-flow evidence behind a GDPR Article 30 record.
An append-only audit log Business+
The Audit Log proves who changed what — data-minimised, and surviving even the deletion of the person who did it.
Unsupported-software register
Tech Radar version-health stands in as your unsupported-software and supply-chain register for NIS2 Article 21.
Honest by construction
Dependra is not a GRC or controls-management tool, and it holds no certifications — it is the evidence engine that helps you satisfy the frameworks you're audited against. Every claim is a “produces evidence for [Article X]” capability statement tied to a field you can verify in-product. Least-privilege access is enforced through a single canonical authorization path, and per-tenant SSO Business+ re-evaluates role and stewardship grants on every login.
See your model read as evidence
Start your trial, model a slice of your estate, and read it as an ISO 27001 asset register or a GDPR Article 30 data-flow record. No payment required to trial.
See the evidence engine