
Stop rebuilding audit evidence. You already have it.
The model that computes blast radius reads, unchanged, as the artefacts auditors ask for. When a regulator asks, you filter and show — instead of assembling a spreadsheet.
One model, read as evidence.
Every application, who uses it and for what, its ownership and lifecycle — captured once.
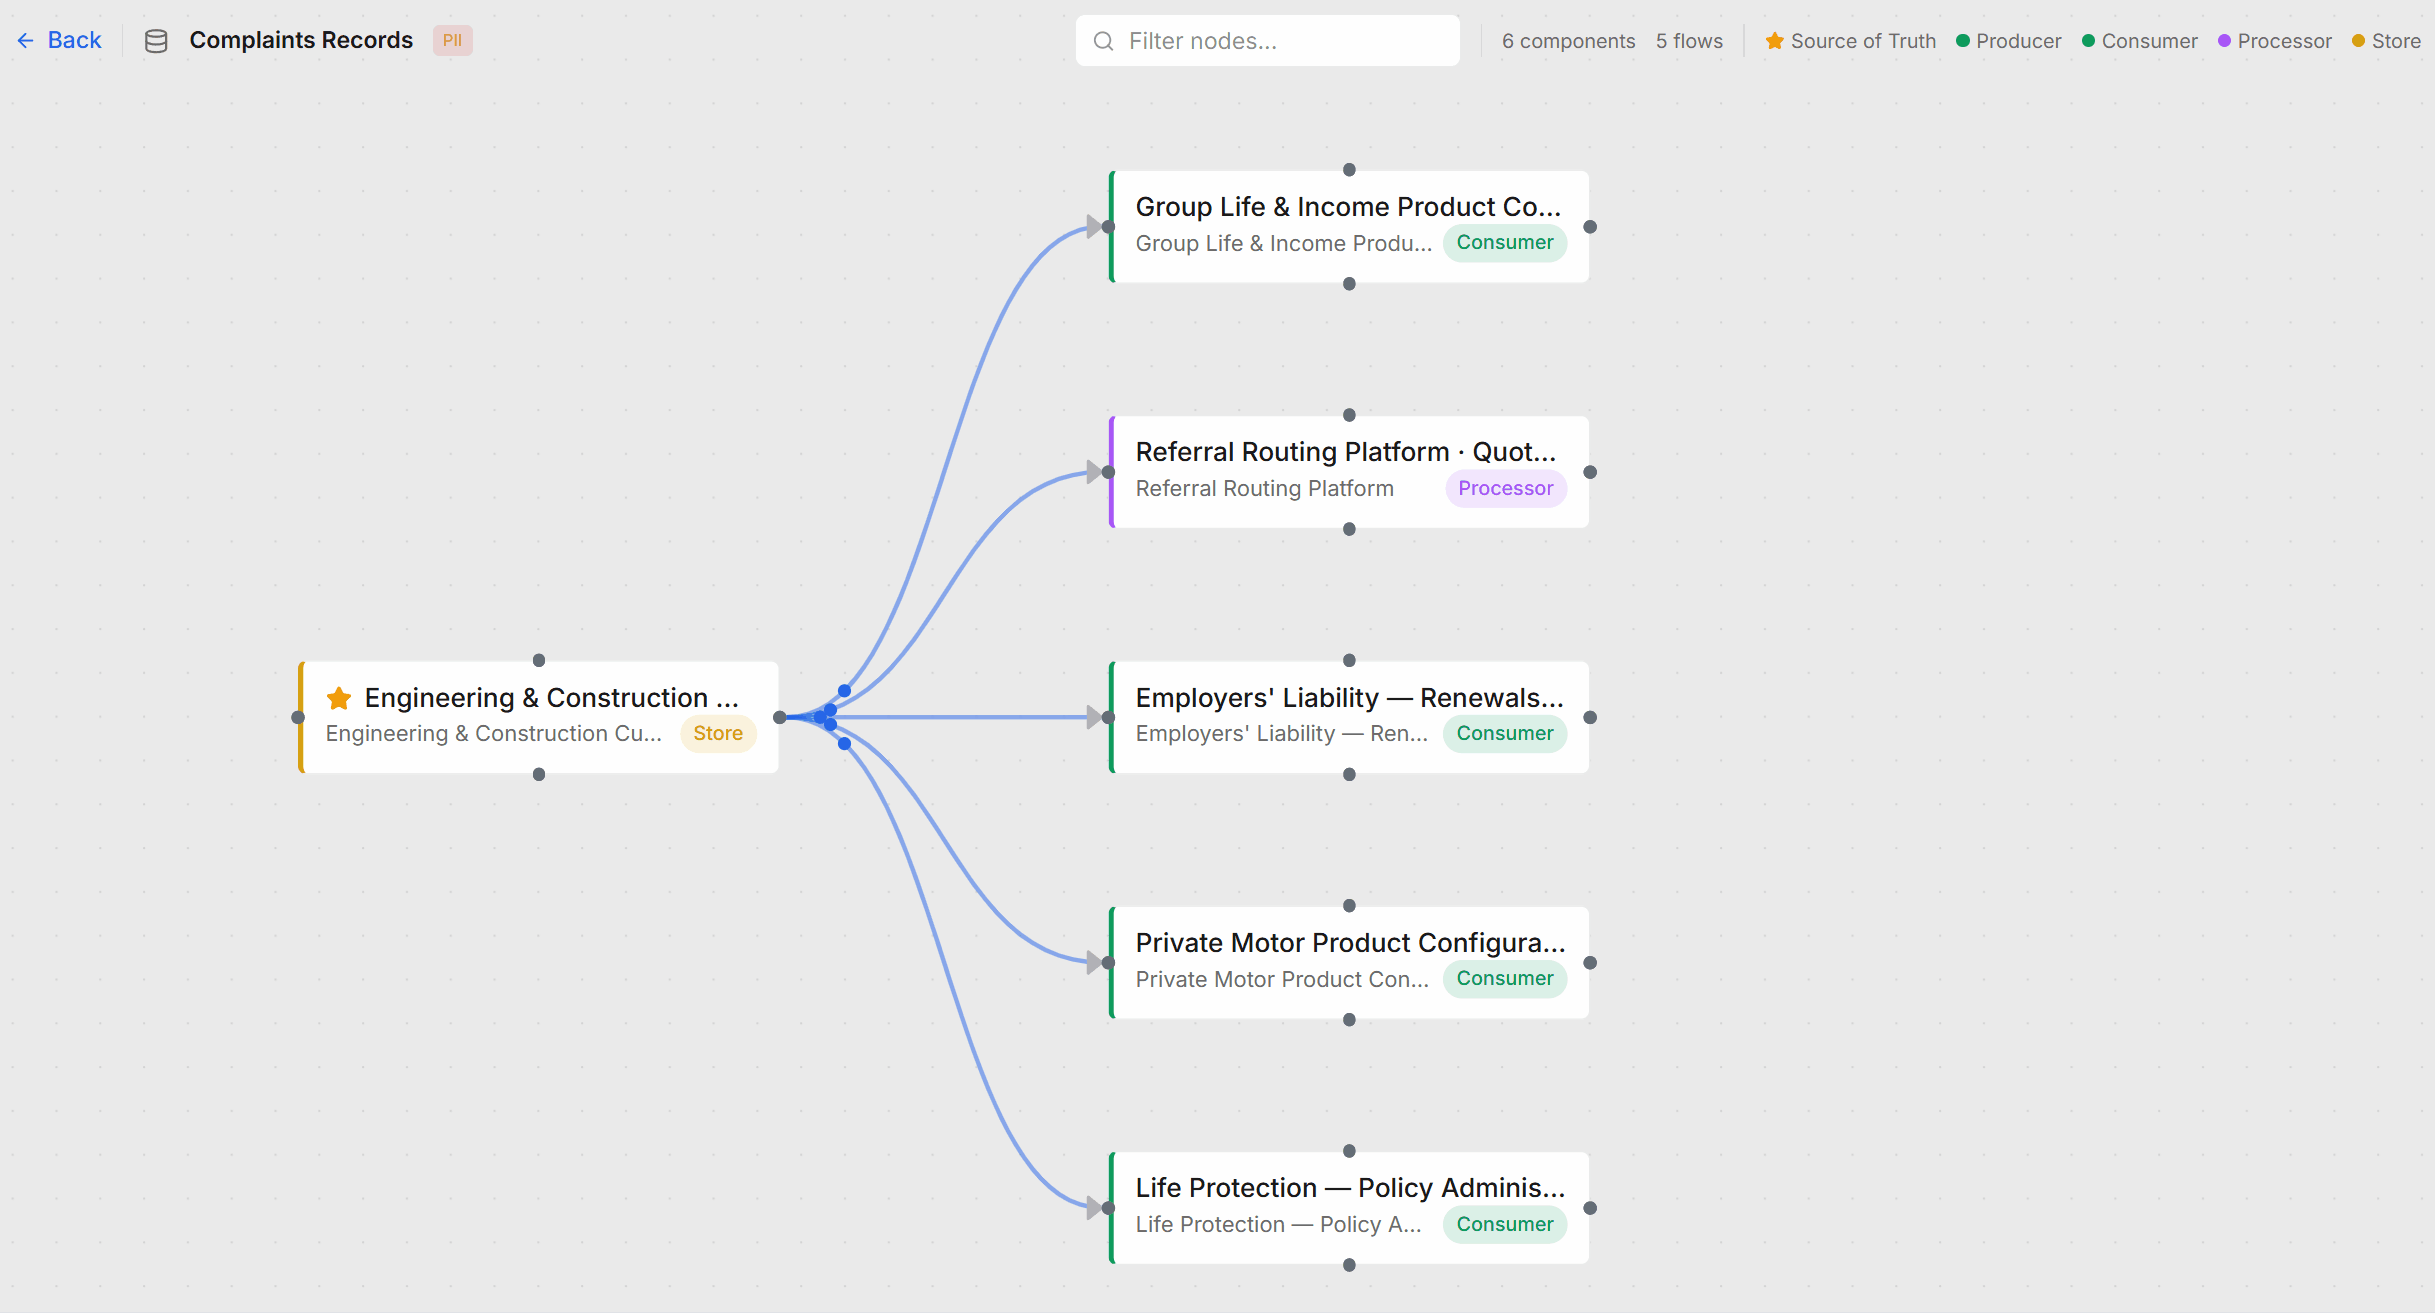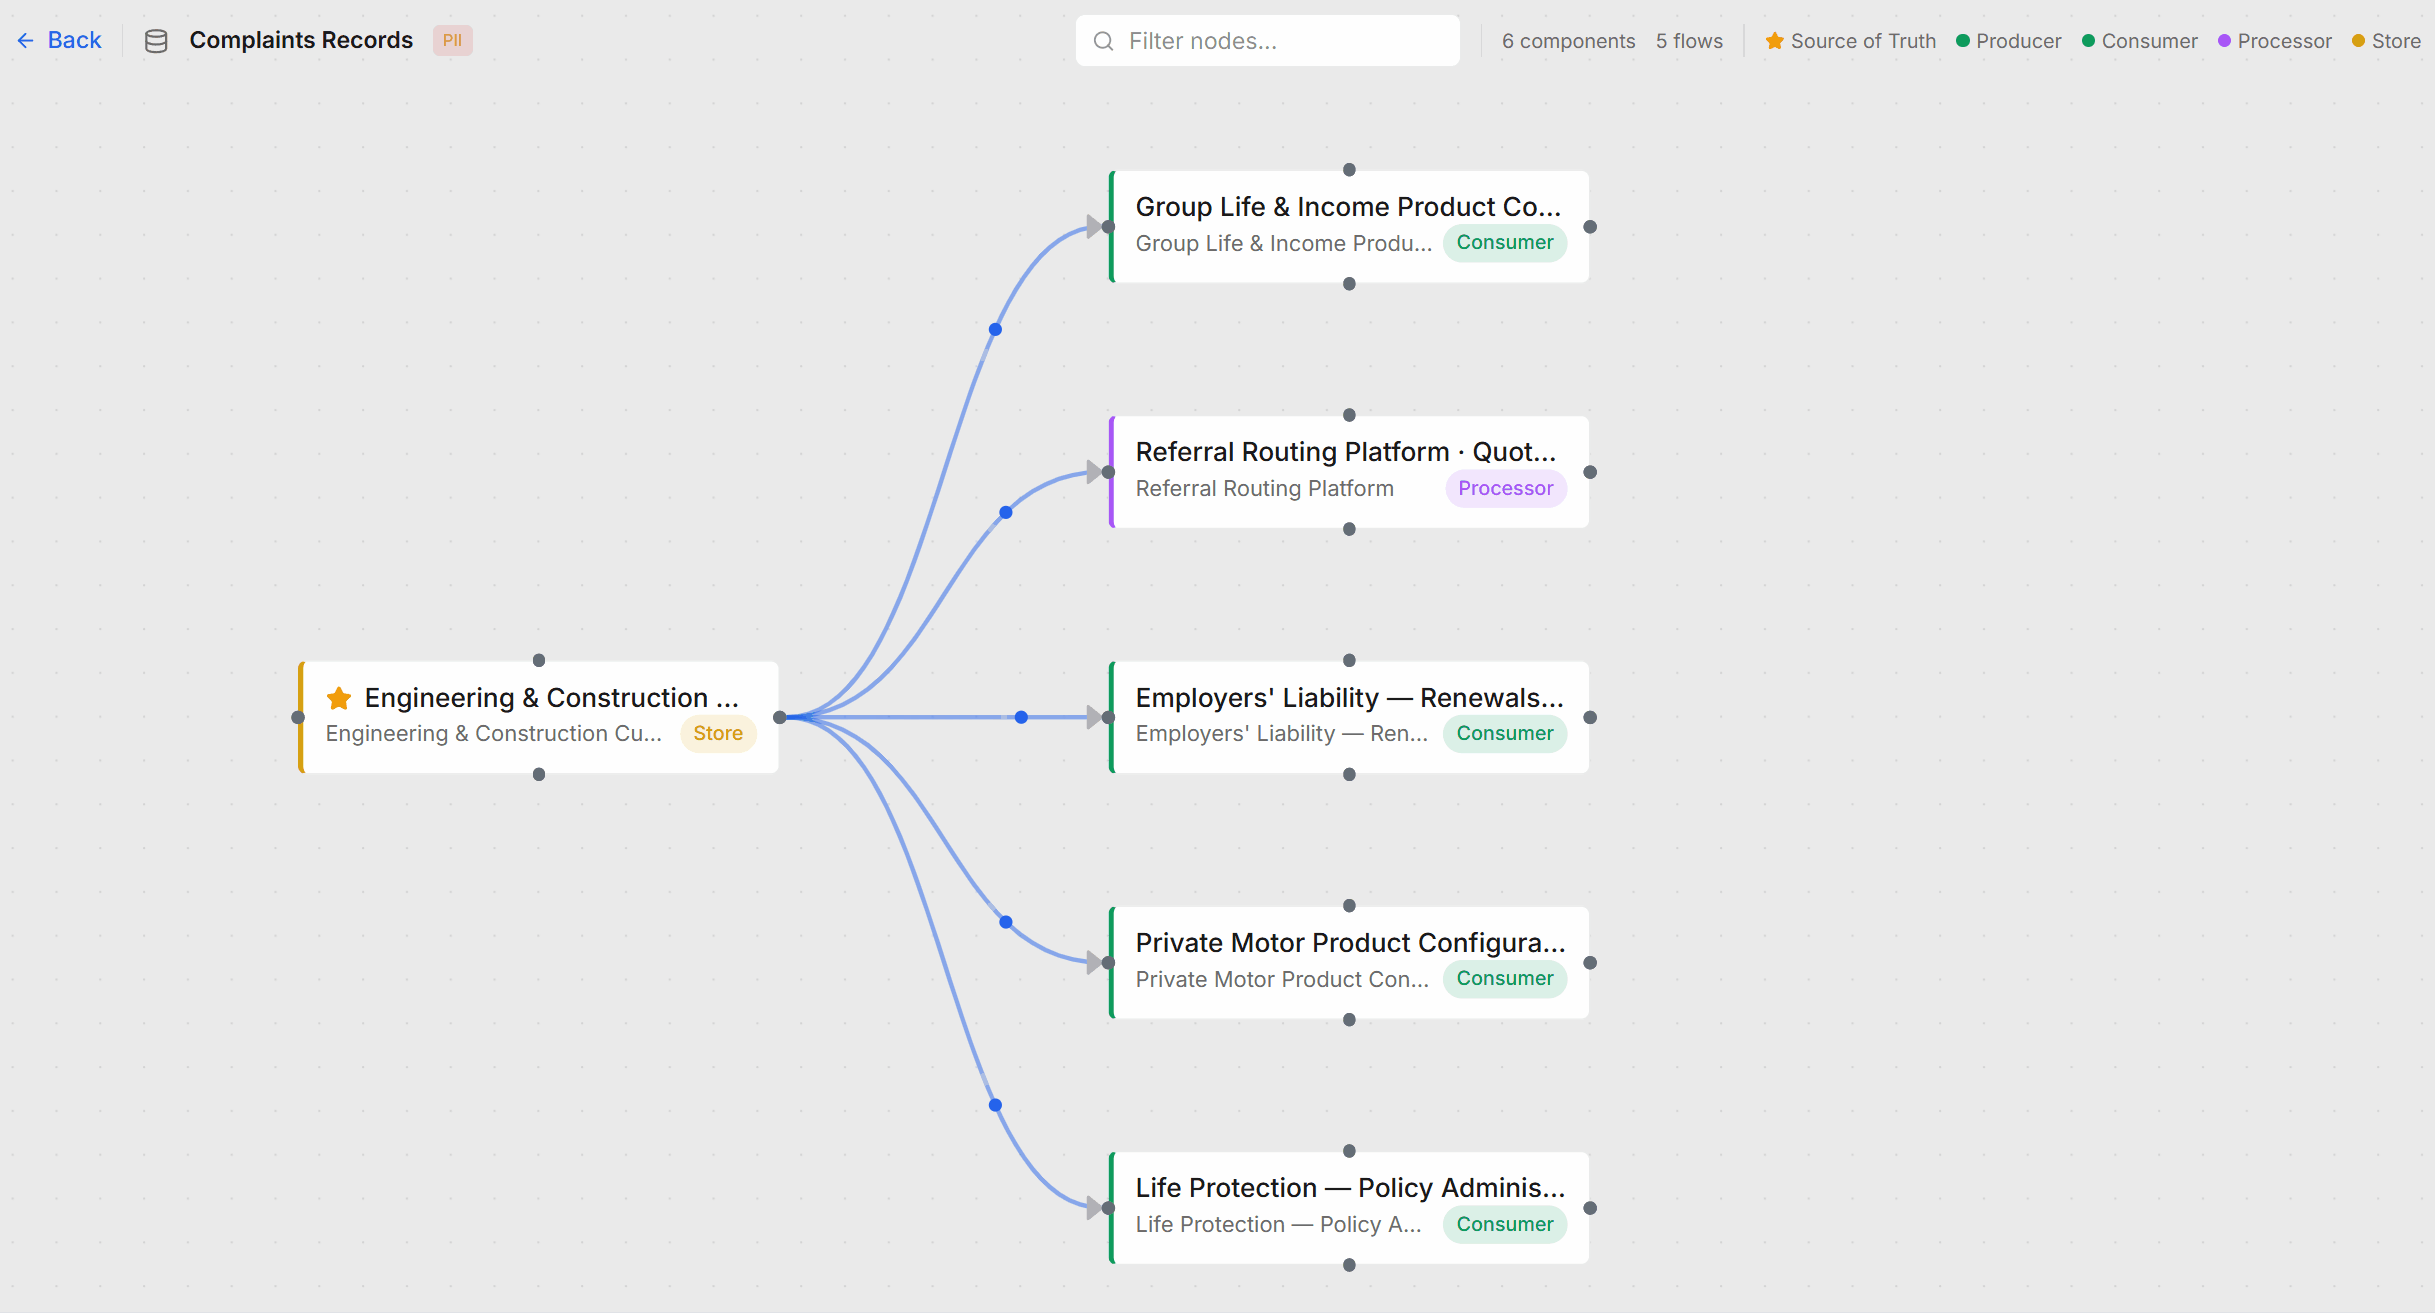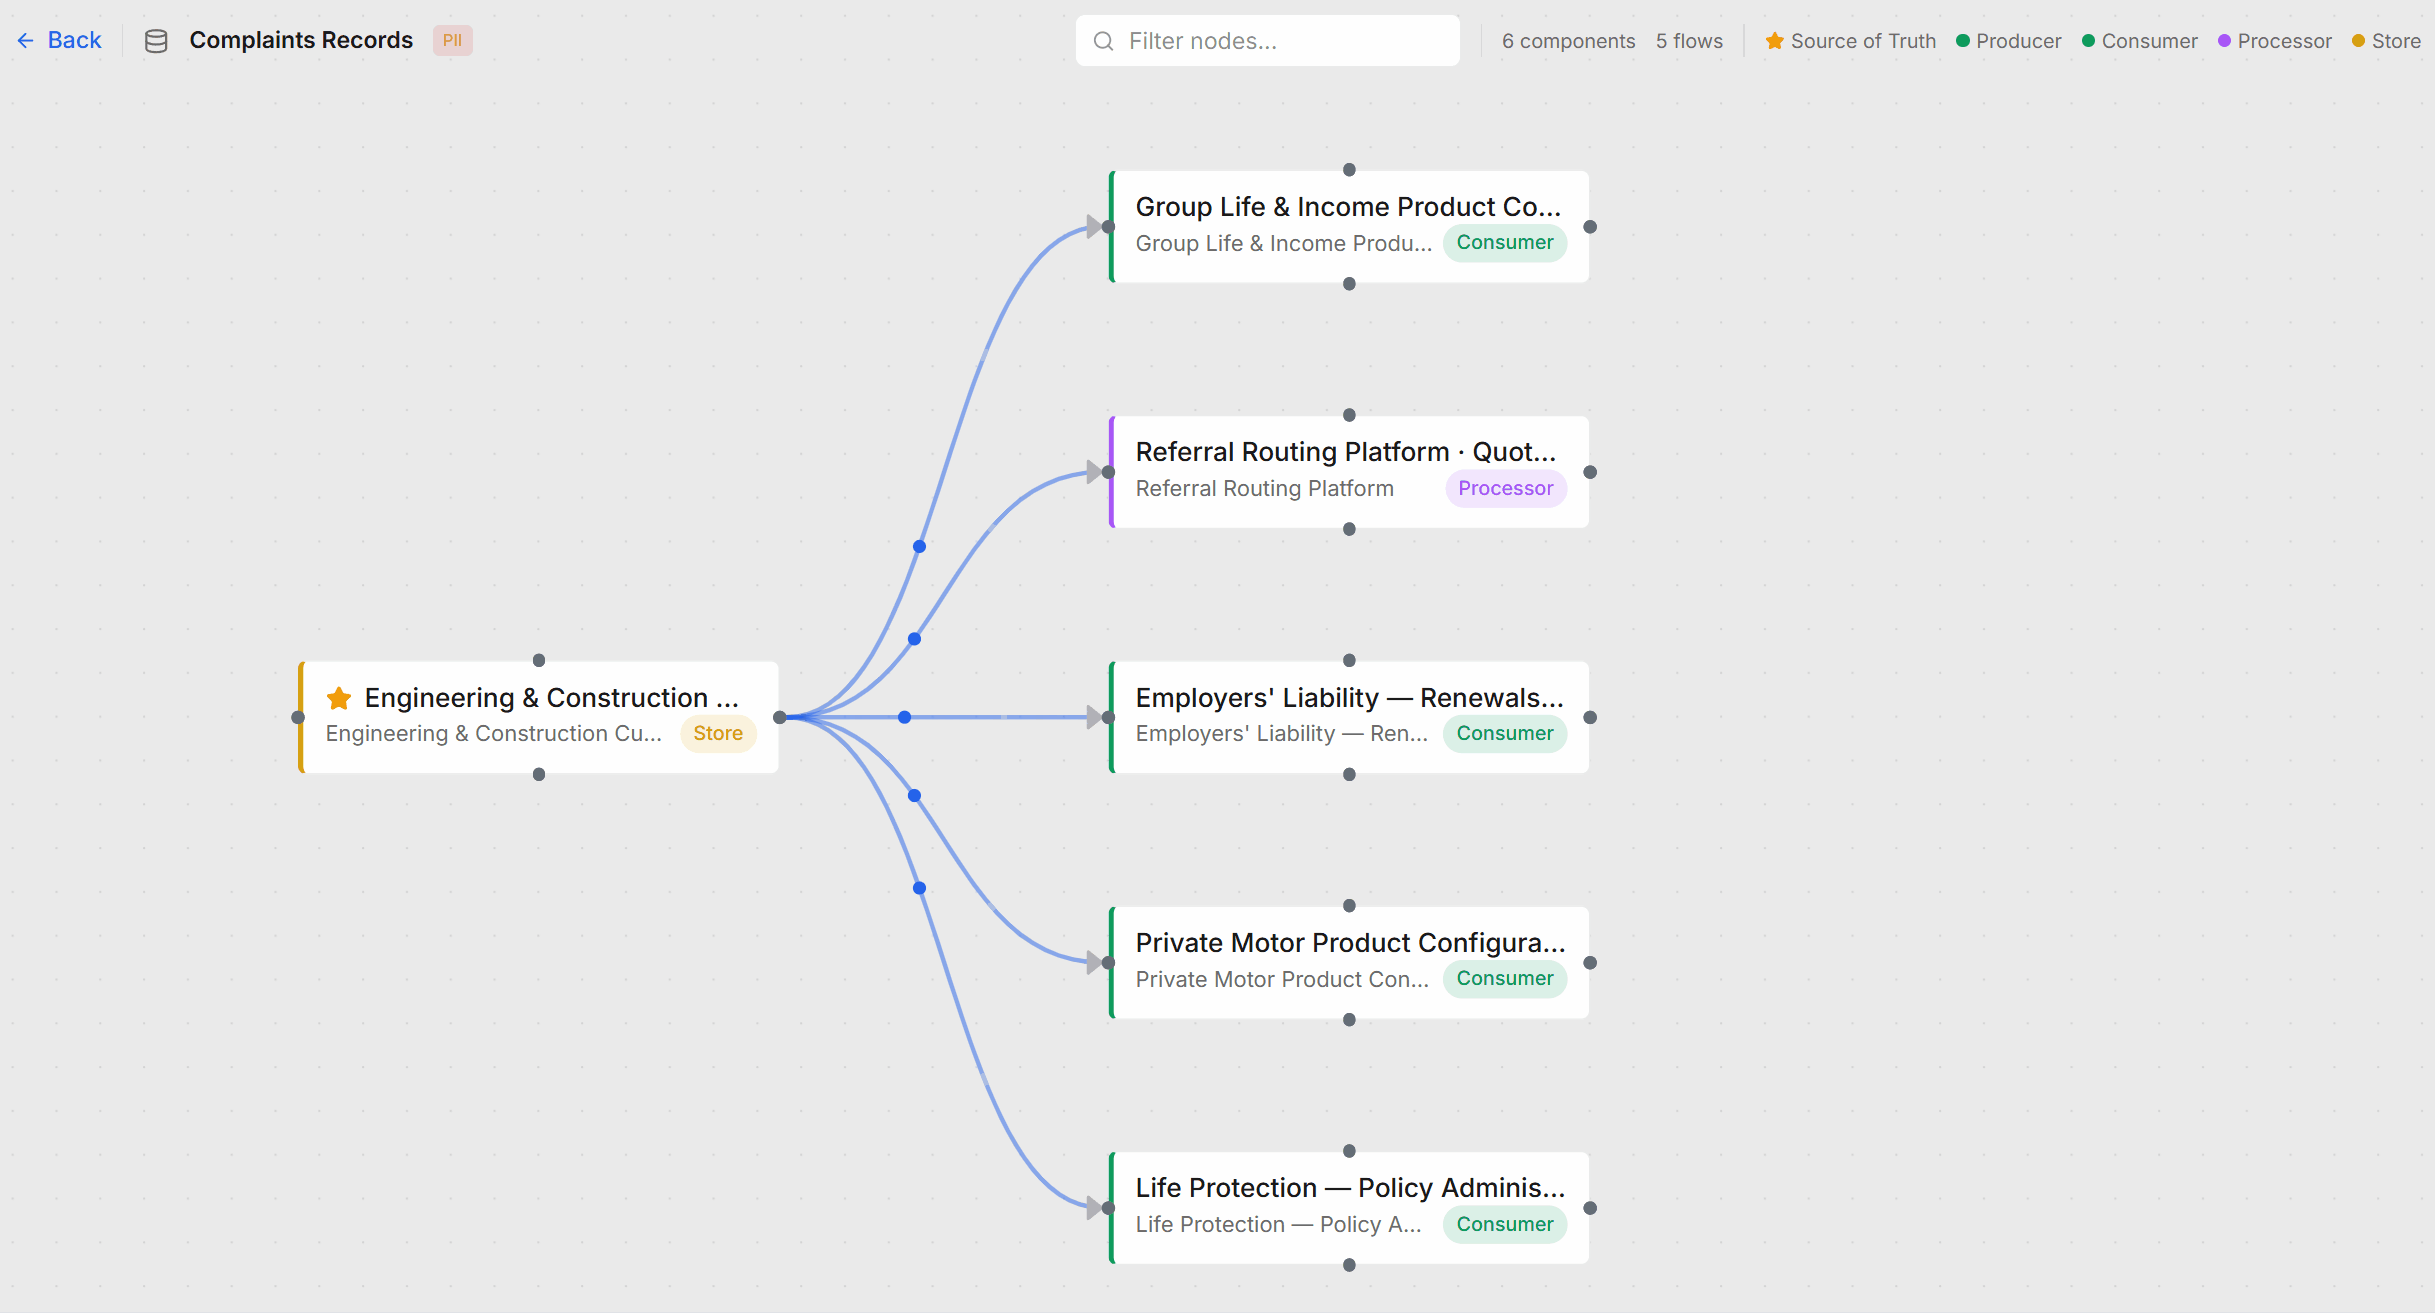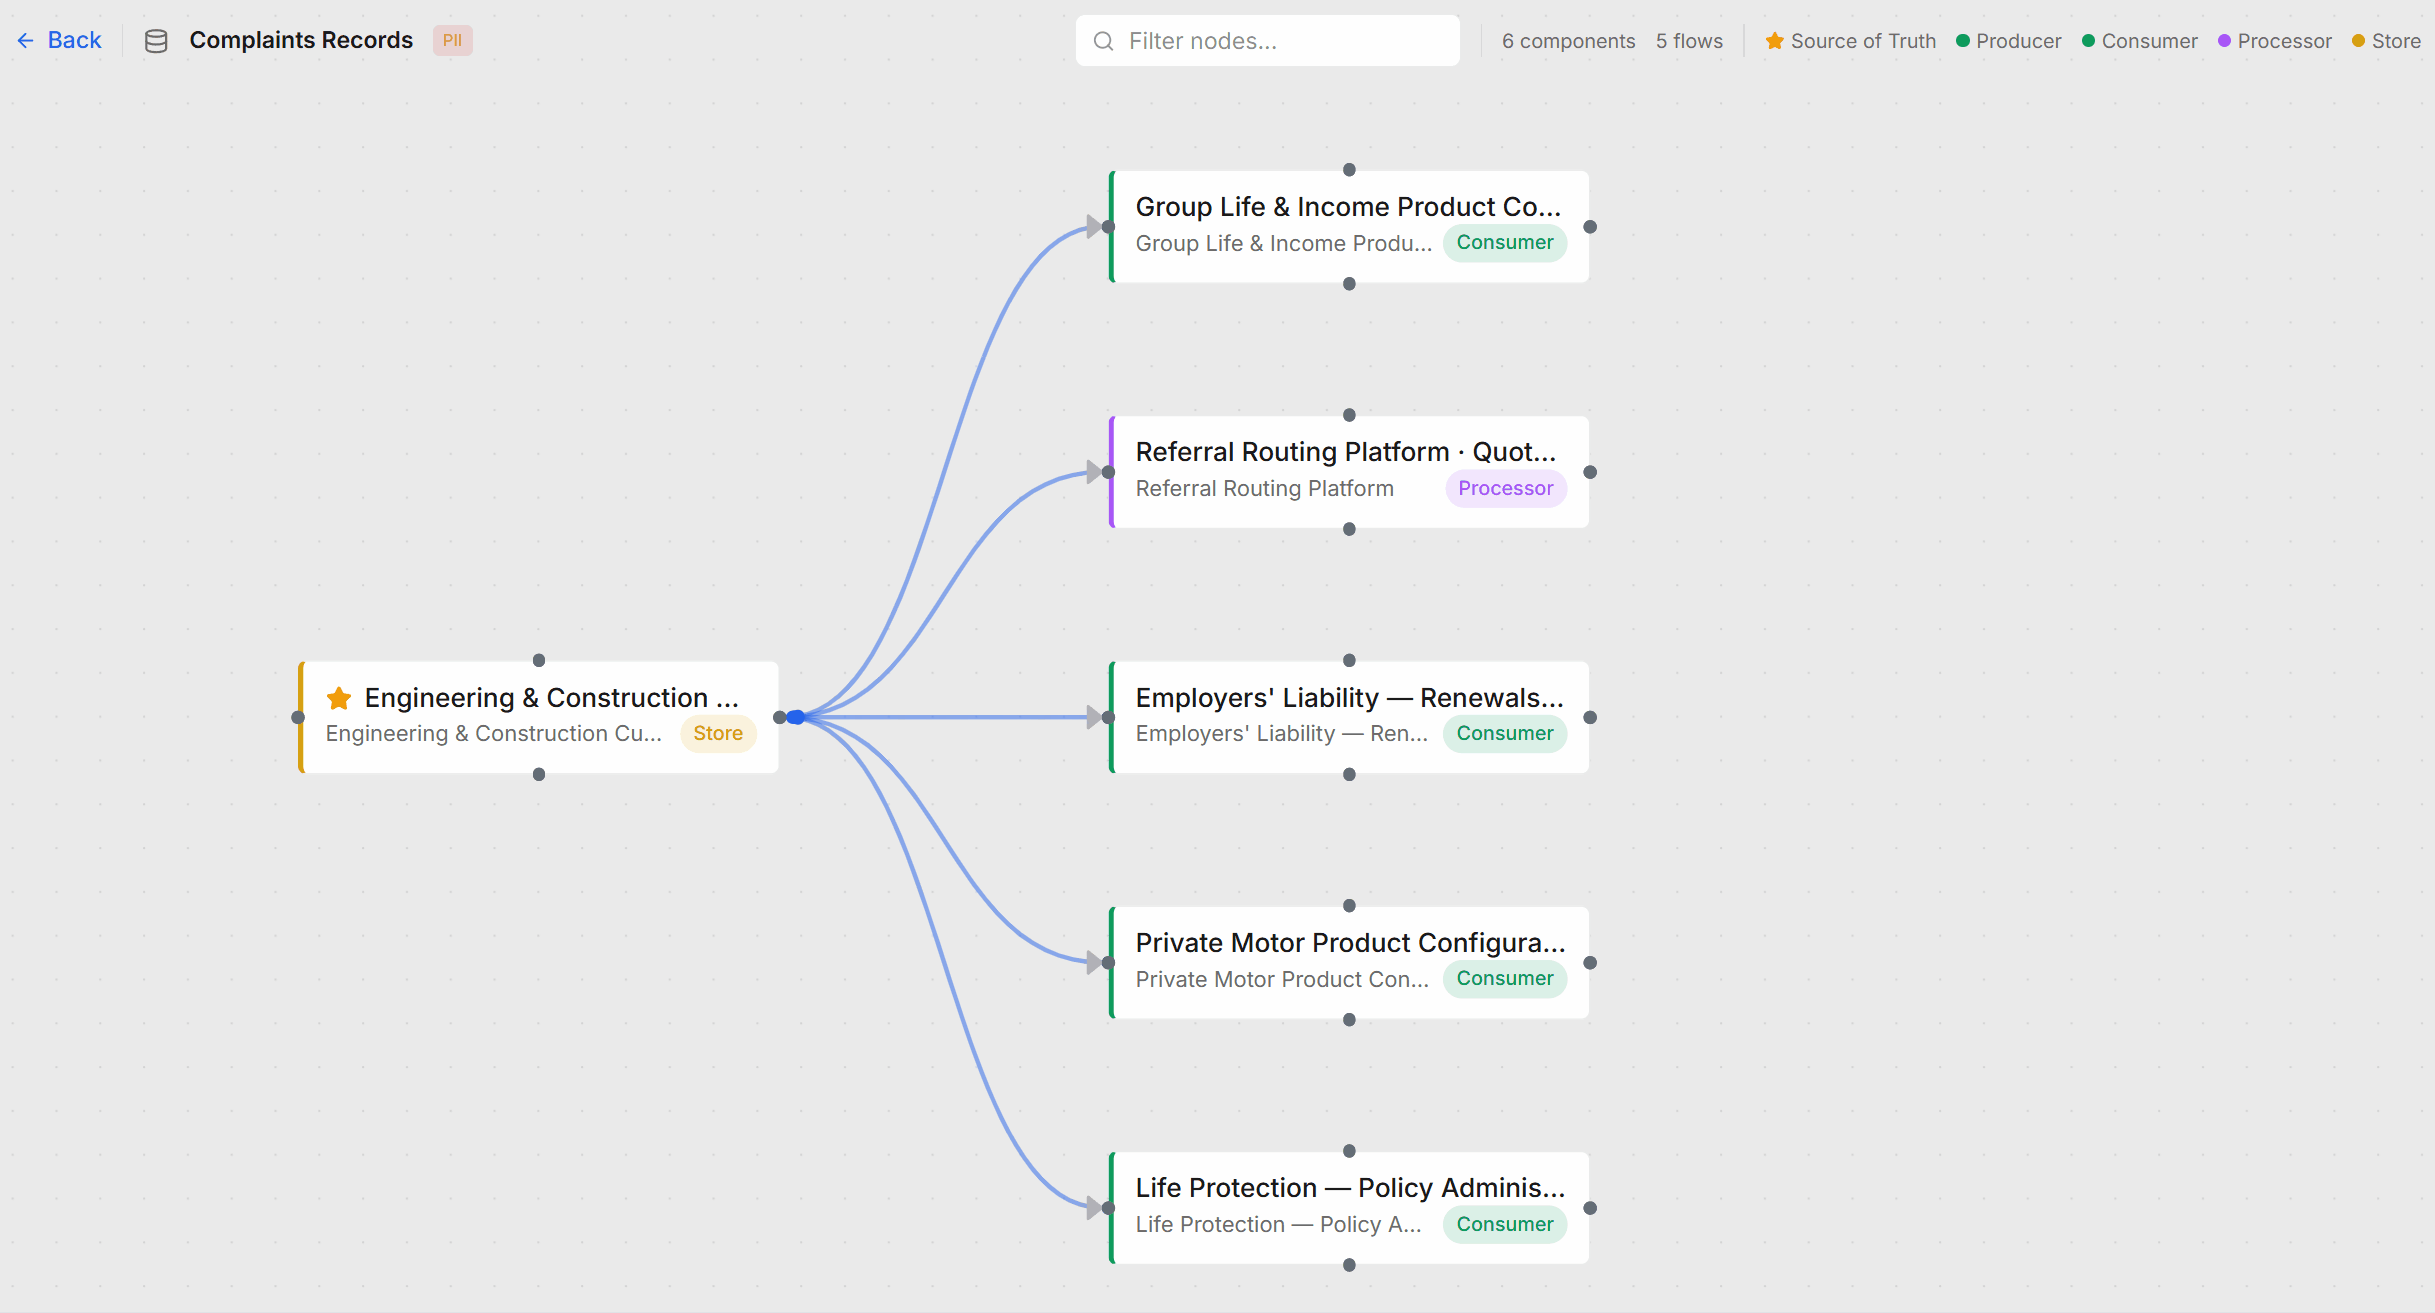
Classification, legal basis, retention and exposure as first-class fields. ICT documentation supports DORA Article 28.
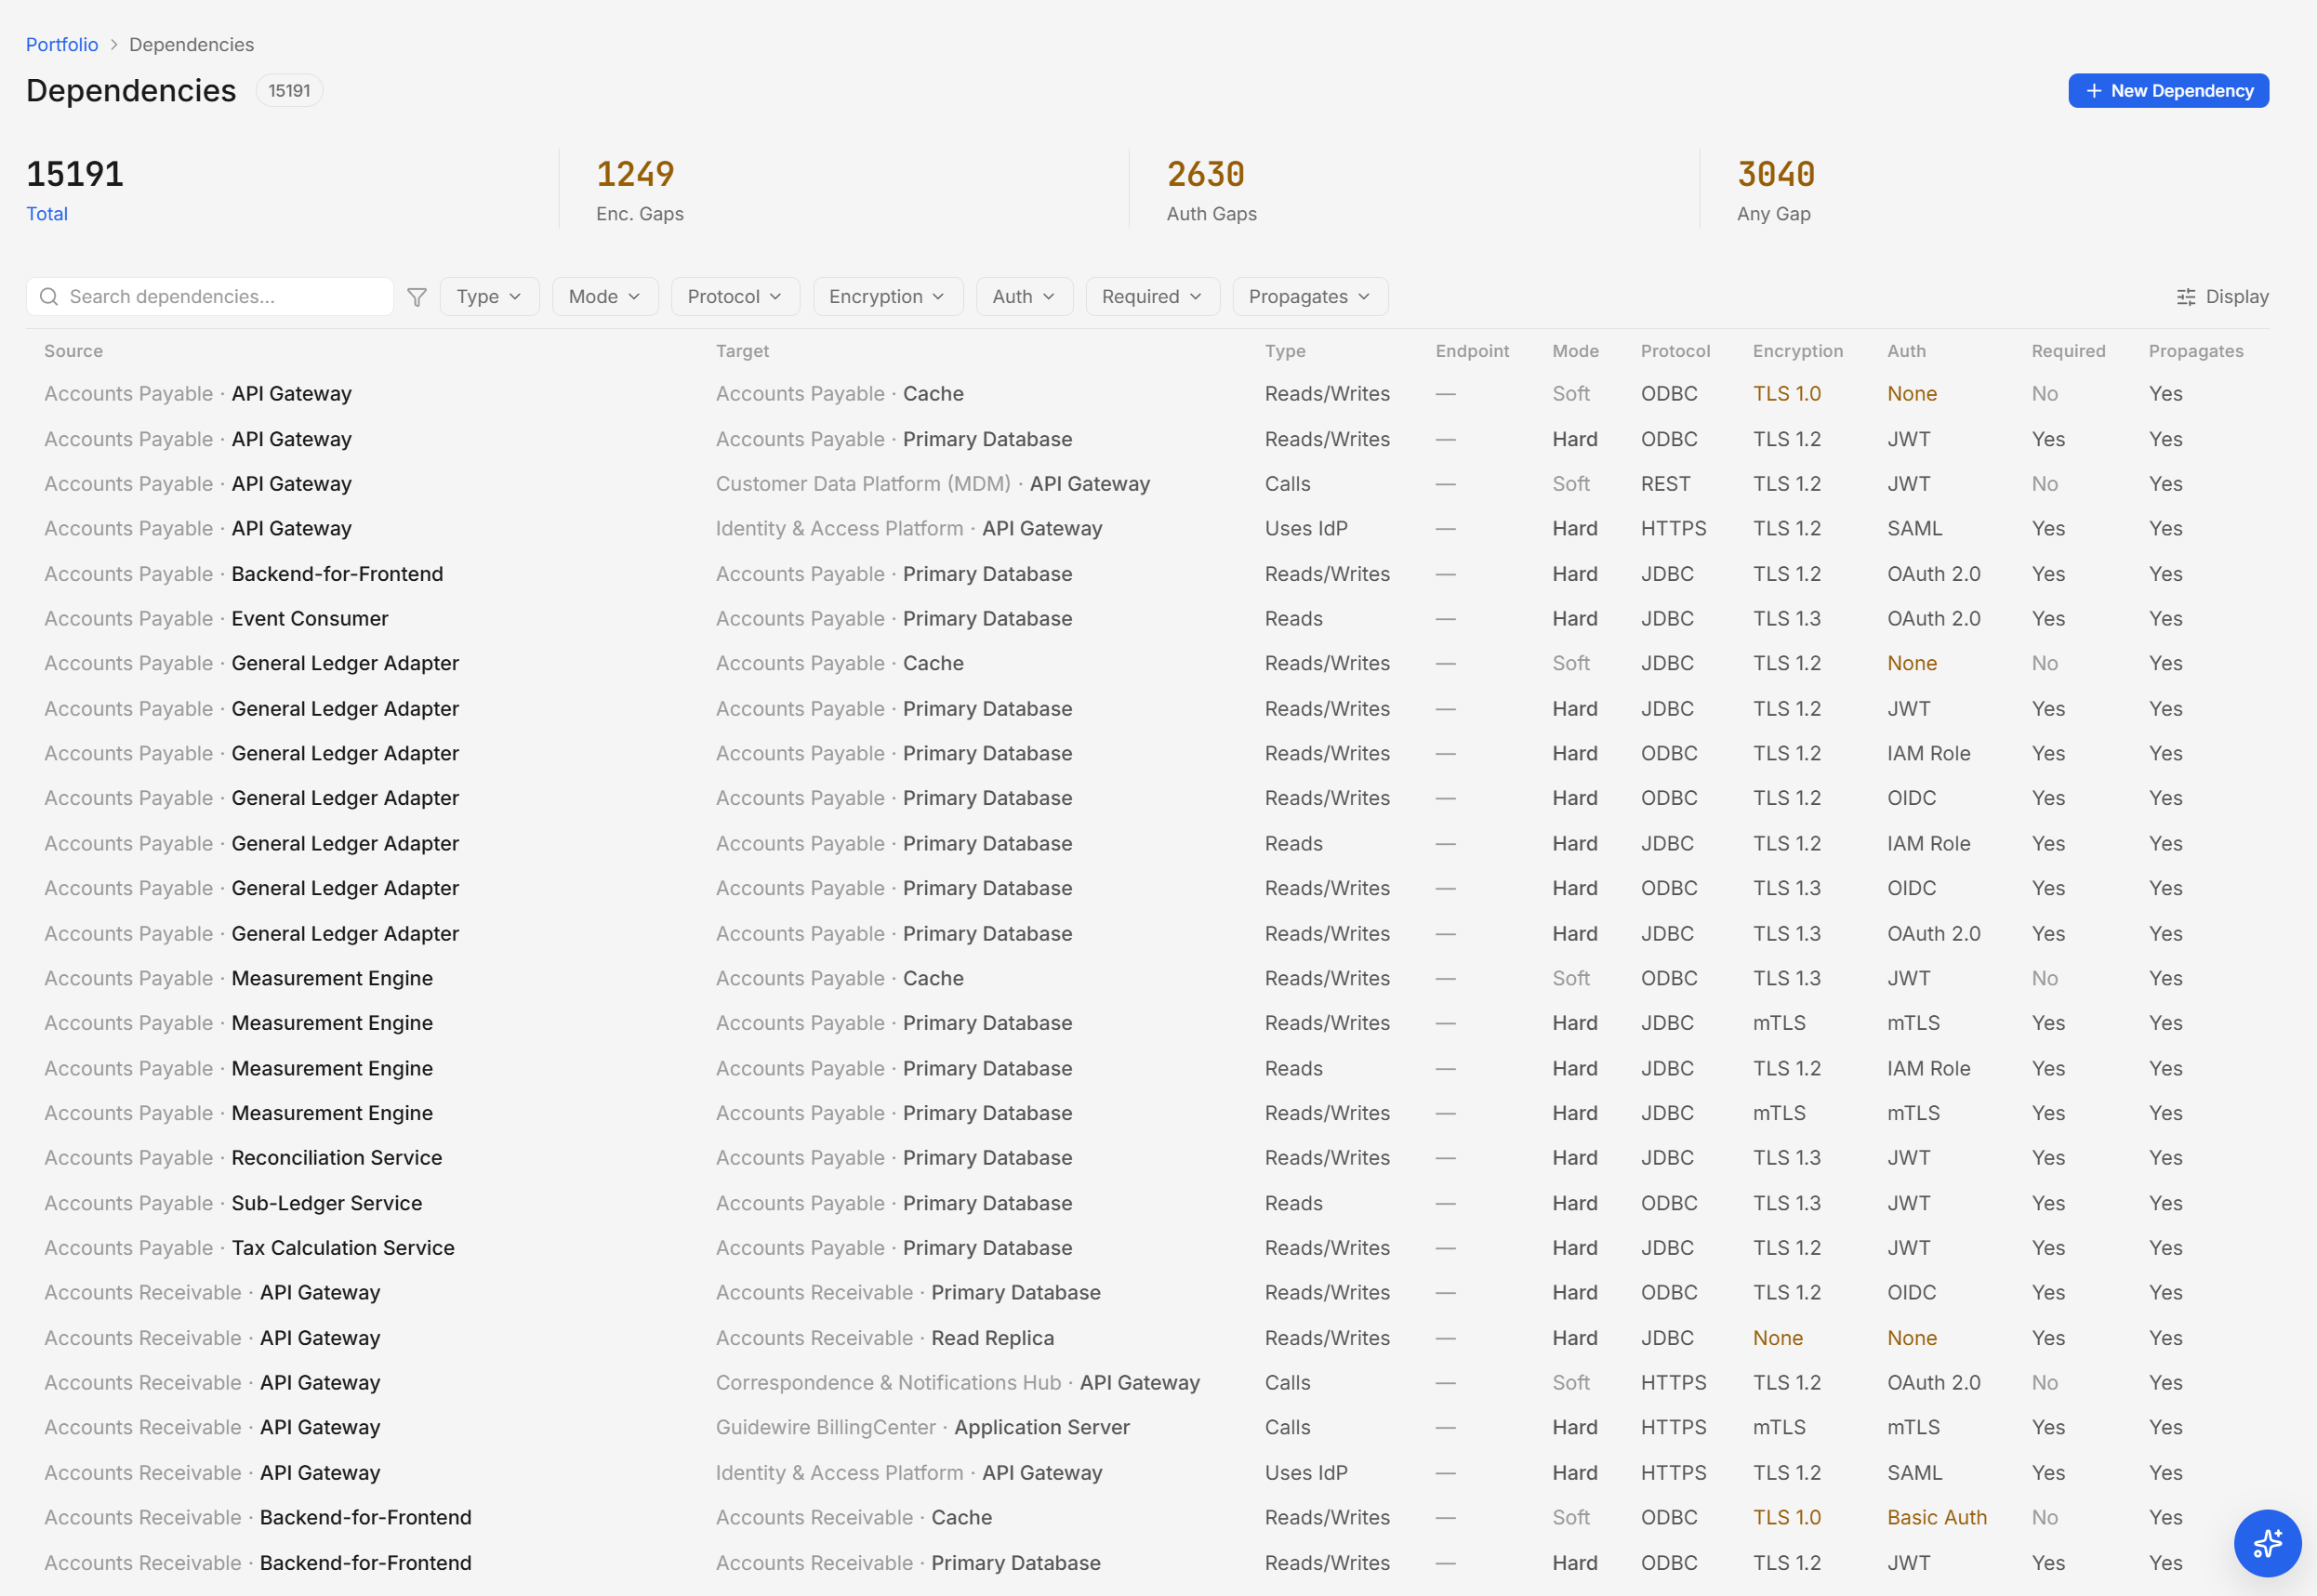
Transport encryption and endpoint auth on every edge; unencrypted paths surface as findings.
Daily end-of-life sync classifies every technology and maps it to the components that run it.
Materialised from component–dataset and dependency links.
Append-only, storing only a short actor signature, so it survives deletion of the actor. Business+.
Honest about scope
Dependra is not a GRC tool and is not certified against any framework. It produces evidence for, never a certification seal. “A GDPR clock just started” means exposure is in scope, not a computed 72-hour countdown.
Tier-aware
Usage register, datasets, dependency register, lineage and tech radar are on every plan. Audit log, risk analysis and process approvals are Business+; SLA tracking is Enterprise.
EU-sovereign
EU-hosted, EU-operated, EU-owned. The model that maps your critical systems never leaves EU jurisdiction.
Security & trust →Let the same data answer your next audit.
Model your estate once. No payment required to trial.